Buy dachsanierung.eu ?
We are moving the project
dachsanierung.eu .
Are you interested in purchasing the domain
dachsanierung.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy dachsanierung.eu ?
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **

Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
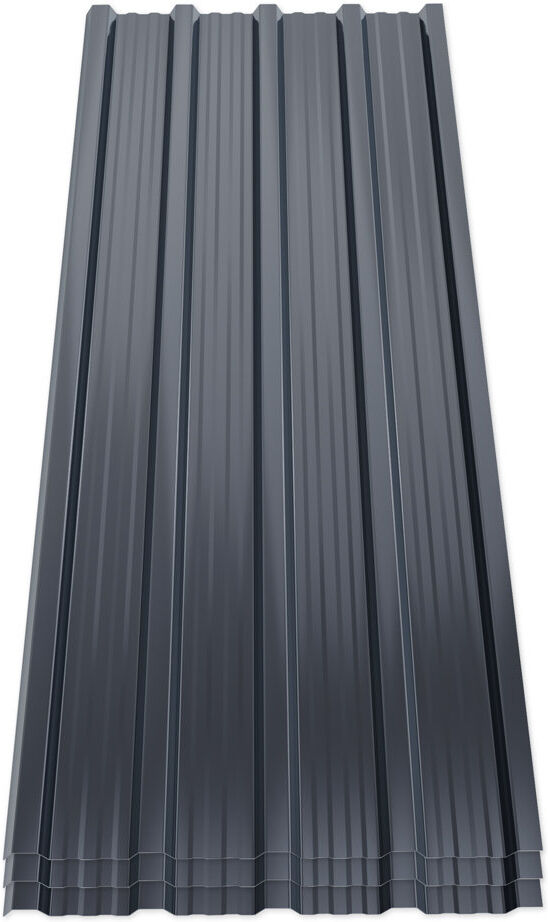
Symple Stuff Metal Roofing KitThis pack of 12 corrugated roof sheets is ideal for all domestic, agricultural, and industrial buildings. The roof sheets are made from rust-proof galvanized metal and have a high load capacity which is perfect for general roofing and walling applications. These roof sheets are 115cm x 45cm in size and 0.3mm in thickness. They are suitable for sheds, workshops, greenhouses, barns, carports, huts, kennels, garages, etc. Note: Please wear gloves when using this product to prevent scratching the fingers. Symple Stuff42,99 £*Shipping: 4,99 £Secure redirect to the provider
-
Dakota Fields Metal Roofing KitAn economical and robust solution for any application, such as sheds, awnings, greenhouses, or garage walls and cladding! The lightweight single-layer roof sheets have no pre-drilled holes, offering flexibility to punch holes for installation according to specific needs, enabling super-fast and easy installation. Dakota Fields59,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Segle Gentle Volcanic Exfoliator Cellular Renovation 50mLA skin-care product for dull skin. From the first application, the gentle volcanic exfoliant improves the appearance of the skin by removing dead cells from the epidermis and excess oil while stimulating cell renewal. This mechanical peeling also brings luminosity to dull or lackluster skin. The skin becomes soft, radiant, and prepared for subsequent treatments.12,17 £*Shipping: 5,28 £Secure redirect to the provider



-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **


How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
What does tpm 20 10 mean?
TPM 20 10 refers to Total Productive Maintenance, a methodology used to improve the effectiveness and efficiency of production equipment. The "20" in TPM 20 10 signifies the 20 pillars or elements of TPM, which are the key principles and activities that contribute to the overall maintenance and improvement of equipment. The "10" in TPM 20 10 represents the 10 basic principles of TPM, which serve as the foundation for implementing and sustaining TPM practices within an organization. Overall, TPM 20 10 is a comprehensive approach to equipment maintenance and improvement, aimed at maximizing productivity and minimizing waste. **
Top-Angebote
Products related to Tpm:
-
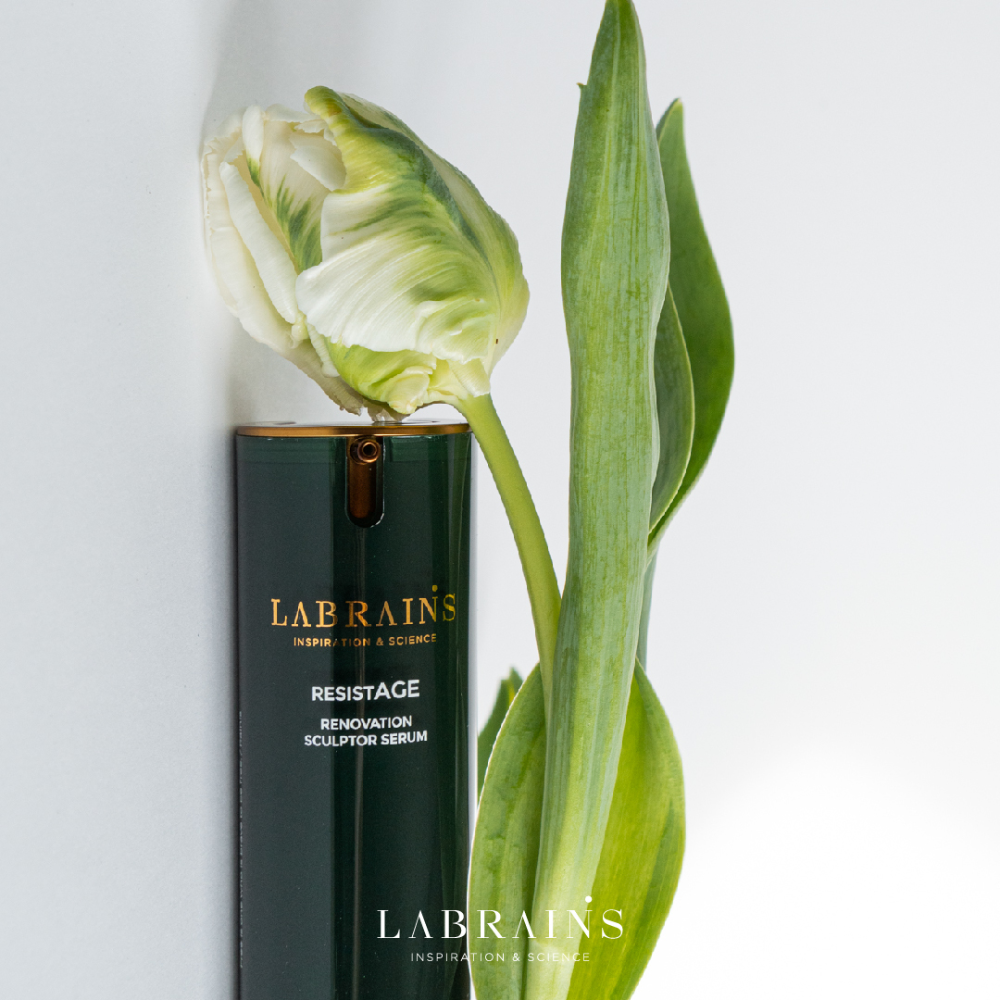
Labrains Renovation Sculptor Cream 50mLA skin-care product for wrinkles and signs of ageing. This product for all types of aging skin. A rich and delicately scented cream has been developed to deeply moisturize and provide high protection. This c ream not only safeguards the skin and its microbiota but also enhances its natural defense system, minimizing the effects of daily and climate-induced stress.71,66 £*Shipping: 5,28 £Secure redirect to the provider
-
Symple Stuff Metal Roofing KitThis pack of 12 corrugated roof sheets is ideal for all domestic, agricultural, and industrial buildings. The roof sheets are made from rust-proof galvanized metal and have a high load capacity which is perfect for general roofing and walling applications. These roof sheets are 115cm x 45cm in size and 0.3mm in thickness. They are suitable for sheds, workshops, greenhouses, barns, carports, huts, kennels, garages, etc. Note: Please wear gloves when using this product to prevent scratching the fingers. Symple Stuff42,99 £*Shipping: 4,99 £Secure redirect to the provider
-
Dakota Fields Metal Roofing KitAn economical and robust solution for any application, such as sheds, awnings, greenhouses, or garage walls and cladding! The lightweight single-layer roof sheets have no pre-drilled holes, offering flexibility to punch holes for installation according to specific needs, enabling super-fast and easy installation. Dakota Fields59,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
Similar search terms for Tpm
-
Segle Gentle Volcanic Exfoliator Cellular Renovation 50mLA skin-care product for dull skin. From the first application, the gentle volcanic exfoliant improves the appearance of the skin by removing dead cells from the epidermis and excess oil while stimulating cell renewal. This mechanical peeling also brings luminosity to dull or lackluster skin. The skin becomes soft, radiant, and prepared for subsequent treatments.12,17 £*Shipping: 5,28 £Secure redirect to the provider
-
Arena Renovation Pc Steam CD Key GlobalArena Renovation: A Game of Restoration Arena Renovation is a video game where you take on the role of a one-person renovation crew. Your mission? To restore dilapidated sports facilities to their former glory. Restoration Tasks : Engage in a variety of tasks such as painting walls, renovating floors, replacing broken chairs, and repairing electrical wiring. Customization : Fill each arena with hundreds of different items, allowing for a high degree of customization. Skill and Tools : Use different skills and tools to assess and meet the needs of each facility. Challenges : The game offers many challenges that require creativity, manual dexterity, and budget planning.6,45 £*Shipping: 0,00 £Secure redirect to the provider
-
Sievert 2960 Roofing Gas Blow Torch BurnerSievert 2960 Roofing Gas Blow Torch Burner - Heavy-Duty Power Burner The Sievert 2960 Roofing Gas Blow Torch Burner is a heavy-duty, lightweight power burner designed for extreme performance in challenging conditions. With an exceptionally strong and windproof flame, this burner is perfect for demanding applications like drying, bitumen laying, field torching, and preheating. Constructed from high-quality stainless steel, the Sievert 2960 is built to withstand the toughest environments, ensuring durability and efficiency for professional use. Pair it with the Sievert Pro neck tubes and 3488 handle for gas-saving pilot flame functionality and instant trigger operation between pilot and main flames. Key Features:43,56 £*Shipping: 5,00 £Secure redirect to the provider
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
What does tpm 20 10 mean?
TPM 20 10 refers to Total Productive Maintenance, a methodology used to improve the effectiveness and efficiency of production equipment. The "20" in TPM 20 10 signifies the 20 pillars or elements of TPM, which are the key principles and activities that contribute to the overall maintenance and improvement of equipment. The "10" in TPM 20 10 represents the 10 basic principles of TPM, which serve as the foundation for implementing and sustaining TPM practices within an organization. Overall, TPM 20 10 is a comprehensive approach to equipment maintenance and improvement, aimed at maximizing productivity and minimizing waste. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.